

Source Permissions and Retrieval Access
Source permissions can restrict which provider files a user may retrieve. Knowledge-base access and provider-file access are separate checks.
Before you begin
A supported source-permission configuration and a user identity that can be mapped for the provider.
Key concepts
Source permissions
Access rules for the original documents or records. Knowledge-base sharing does not necessarily grant access to every source.
Authorization
The decision whether a caller can perform an operation on a resource. Check roles, scopes, organization context, and sharing when access is denied.
User identity
The authenticated person or application acting on a resource. It determines access; a display name or conversation ID does not authenticate a caller.
Connection
A saved authorization to a particular provider account. An action uses the selected account’s access, subject to StackAI sharing controls.
Check access to source content
Review access to the knowledge base itself.
Enable and configure supported source-permission filtering for the retrieval path.
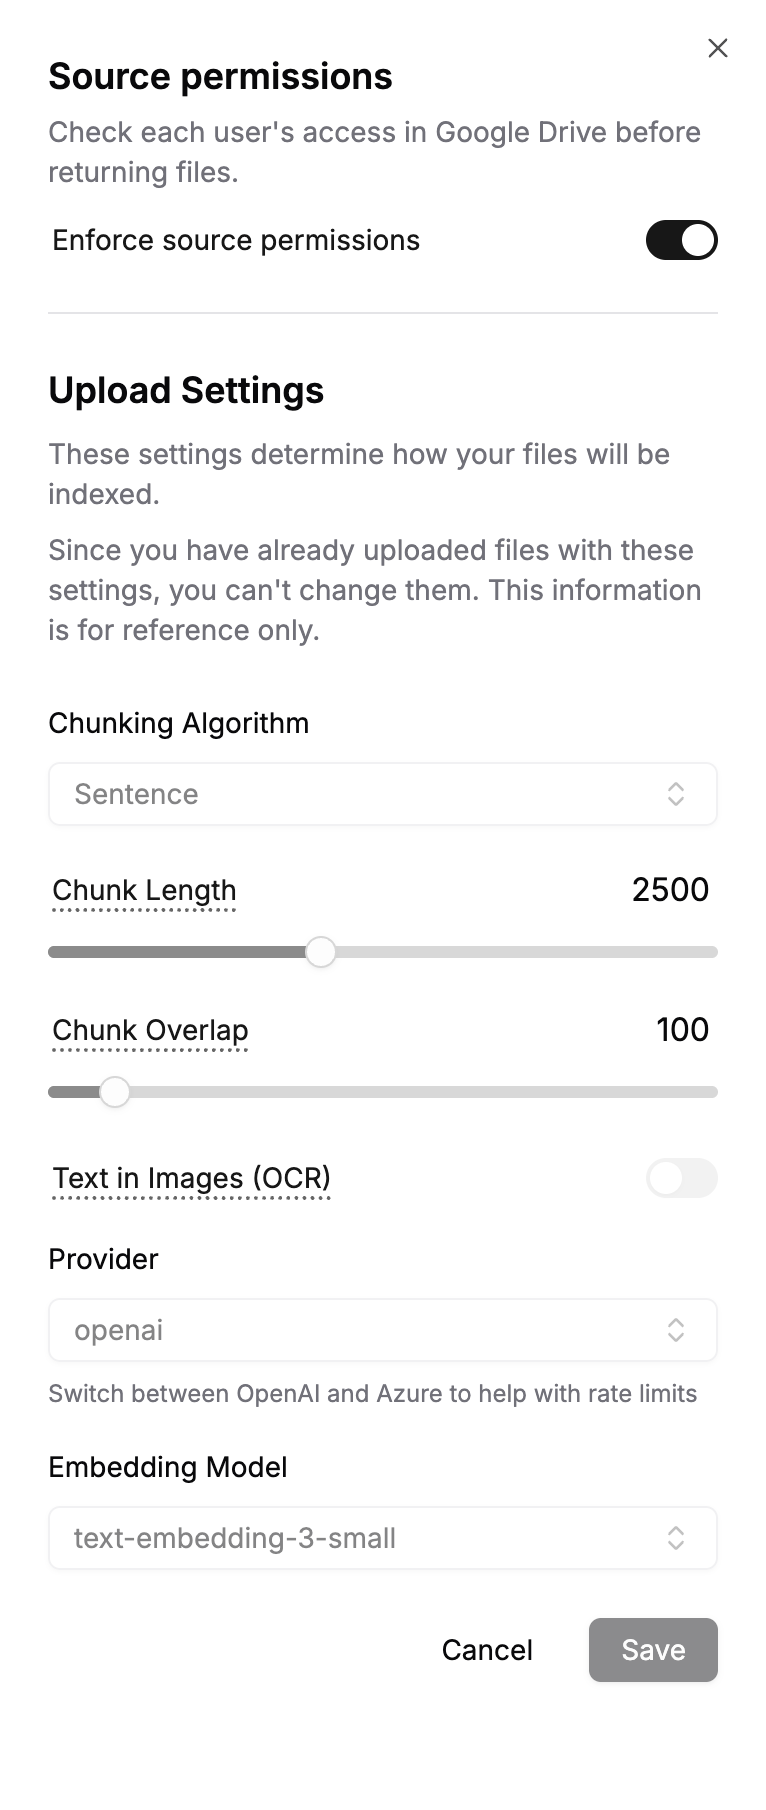
Enable Enforce source permissions for a supported connected knowledge base.
Inspect retrieval using the intended user’s access level and confirm the returned sources.
The configured retrieval path applies the relevant knowledge-base and source access checks.
Behavior and limitations
Granting access to a knowledge base does not always grant access to every source file. Conversely, a provider credential used for background synchronization is not proof of the end user’s access. Permission behavior depends on the provider, selected node, and identity configuration. Do not treat an owner’s successful query as evidence for all viewers.
Related resources
Was this helpful?